

2022 Valid PAM-DEF Dumps for Helping Passing CyberArk Exam!
Download Free CyberArk PAM-DEF Exam Questions & Answer
NEW QUESTION 94
DRAG DROP
Match each component to its respective Log File location.
Answer:
Explanation:
NEW QUESTION 95
An auditor initiates a live monitoring session to PSM server to view an ongoing live session.
When the auditor's machine makes an RDP connection the PSM server, which user will be used?
- A. Credentials stored in the Vault for the target machine
- B. PSMAdminConnect
- C. Shadowuser
- D. PSMConnect
Answer: B
NEW QUESTION 96
DRAG DROP
Match each key to its recommended storage location.
Answer:
Explanation: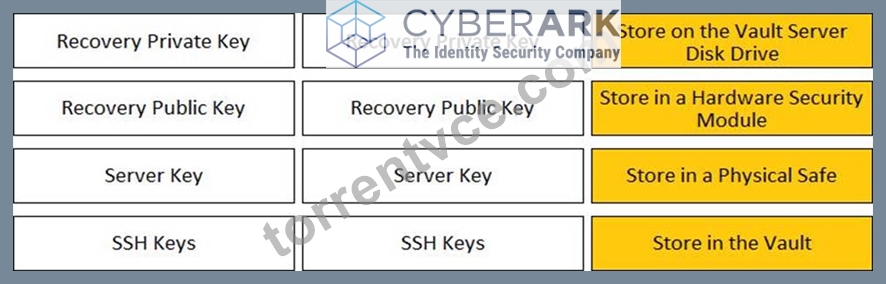
NEW QUESTION 97
If the AccountUploader Utility is used to create accounts with SSH keys, which parameter do you use to set the full or relative path of the SSH private key file that will be attached to the account?
- A. Address
- B. KeyFile
- C. KeyPath
- D. ObjectName
Answer: B
NEW QUESTION 98
You are onboarding an account that is not supported out of the box.
What should you do first to obtain a platform to import?
- A. Create a service ticket in the customer portal explaining the requirements of the custom platform.
- B. Visit the CyberArk marketplace and search for a platform that meets your needs.
- C. From the platforms page, uncheck the "Hide non-supported platforms" checkbox and see if a platform meeting your needs appears.
- D. Search common community portals like stackoverflow, reddit, github for an existing platform.
Answer: A
NEW QUESTION 99
Users are unable to launch Web Type Connection components from the PSM server. Your manager asked you to open the case with CyberArk Support.
Which logs will help the CyberArk Support Team debug the issue? (Choose three.)
- A. <Session_ID>.Component.log
- B. PSMConsole.log
- C. ITAlog.log
- D. PSMDebug.log
- E. PSMTrace.log
- F. PMconsole.log
Answer: C,D,E
NEW QUESTION 100
A user requested access to view a password secured by dual-control and is unsure who to contact to expedite the approval process. The Vault Admin has been asked to look at the account and identify who can approve their request.
What is the correct location to identify users or groups who can approve?
- A. PVWA> Administration > Platform Configuration > Edit Platform > UI & Workflow > Dual Control> Approvers
- B. PVWA> Policies > Access Control (Safes) > Safe Members > Workflow > Authorize Password Requests
- C. PVWA> Account List > Edit > Show Advanced Settings > Dual Control > Direct Managers
- D. PrivateArk > Admin Tools > Users and Groups > Auditors (Group Membership)
Answer: B
NEW QUESTION 101
A Simple Mail Transfer Protocol (SMTP) integration is critical for monitoring Vault activity and facilitating workflow processes, such as Dual Control.
- A. False
- B. True
Answer: A
NEW QUESTION 102
Which type of automatic remediation can be performed by the PTA in case of a suspected credential theft security event?
- A. Session suspension
- B. Password change
- C. Session termination
- D. Password reconciliation
Answer: B
NEW QUESTION 103
A Reconcile Account can be specified in the Master Policy.
- A. FALSE
- B. TRUE
Answer: A
NEW QUESTION 104
Which report could show all accounts that are past their expiration dates?
- A. Activity log
- B. Application Inventory report
- C. Privileged Account Compliance Status report
- D. Privileged Account Inventory report
Answer: C
NEW QUESTION 105
The vault supports Role Based Access Control.
- A. FALSE
- B. TRUE
Answer: A
NEW QUESTION 106
You are onboarding 5,000 UNIX root accounts for rotation by the CPM. You discover that the CPM is unable to log in directly with the root account and will need to use a secondary account.
How should this be configured to allow for password management using least privilege?
- A. Configure each CPM to use the correct logon account.
- B. Configure the UNIX platform to use the correct logon account.
- C. Configure each CPM to use the correct reconcile account.
- D. Configure the UNIX platform to use the correct reconcile account.
Answer: B
NEW QUESTION 107
DRAG DROP
Match each permission to where it can be found.
Answer:
Explanation:
NEW QUESTION 108
Which combination of Safe member permissions will allow end users to log in to a remote machine transparently but NOT show or copy the password?
- A. Use Accounts, List Accounts
- B. List Accounts, Retrieve Accounts
- C. Use Accounts, Retrieve Accounts, List Accounts
- D. Use Accounts
Answer: B
NEW QUESTION 109
Your organization requires all passwords be rotated every 90 days.
Where can you set this regulatory requirement?
- A. PVWAConfig.xml
- B. Safe Templates
- C. Platform Configuration
- D. Master Policy
Answer: D
NEW QUESTION 110
One can create exceptions to the Master Policy based on ____________________.
- A. Safes
- B. Platforms
- C. Policies
- D. Accounts
Answer: B
NEW QUESTION 111
Accounts Discovery allows secure connections to domain controllers.
- A. FALSE
- B. TRUE
Answer: A
NEW QUESTION 112
A new HTML5 Gateway has been deployed in your organization.
Where do you configure the PSM to use the HTML5 Gateway?
- A. Administration > Options > Privileged Session Management > Configured PSM Servers > Connection Details
- B. Administration > Options > Privileged Session Management > Configured PSM Servers > Add PSM Gateway
- C. Administration > Options > Privileged Session Management > Add Configured PSM Gateway Servers
- D. Administration > Options > Privileged Session Management > Configured PSM Servers > Connection Details > Add PSM Gateway
Answer: D
NEW QUESTION 113
If a user is a member of more than one group that has authorizations on a safe, by default that user is granted________.
- A. the vault will not allow this situation to occur.
- B. only those permissions that exist on the group added to the safe first.
- C. only those permissions that exist in all groups to which the user belongs.
- D. the cumulative permissions of all groups to which that user belongs.
Answer: D
NEW QUESTION 114
Which PTA sensors are required to detect suspected credential theft?
- A. Logs, Vault Logs
- B. Logs, Network Sensor, Vault Logs
- C. Logs, Network Sensor, EPM
- D. Logs, PSM Logs, CPM Logs
Answer: A
NEW QUESTION 115
What is the configuration file used by the CPM scanner when scanning UNIX/Linux devices?
- A. PVConfig.xml
- B. plink.exe
- C. dbparm.ini
- D. UnixPrompts.ini
Answer: D
NEW QUESTION 116
When running a "Privileged Accounts Inventory" Report through the Reports page in PVWA on a specific safe, which permission/s are required on that safe to show complete account inventory information?
- A. Manage Safe Owners
- B. List Accounts, View Safe Members
- C. List Accounts, Access Safe without confirmation
- D. Manage Safe, View Audit
Answer: B
NEW QUESTION 117
SAFE Authorizations may be granted to____________.
Select all that apply.
- A. LDAP Groups
- B. LDAP Users
- C. Vault Users
- D. Vault Group
Answer: A,B,C,D
NEW QUESTION 118
Which user(s) can access all passwords in the Vault?
- A. Administrator
- B. Any member of auditors
- C. Master
- D. Any member of Vault administrators
Answer: C
NEW QUESTION 119
......
PAM-DEF Exam Dumps For Certification Exam Preparation: https://www.torrentvce.com/PAM-DEF-valid-vce-collection.html
Online VALID PAM-DEF Exam Dumps File Instantly: https://drive.google.com/open?id=10-3S4LcpetIz0NK1EKkC6379ny2ajXG0