
PECB ISO-IEC-27001-Lead-Auditor日本語 : PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor日本語版)

- Exam Code: ISO-IEC-27001-Lead-Auditor日本語
- Exam Name: PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor日本語版)
- Updated: Nov 18, 2026
About PECB ISO-IEC-27001-Lead-Auditor日本語 Exam
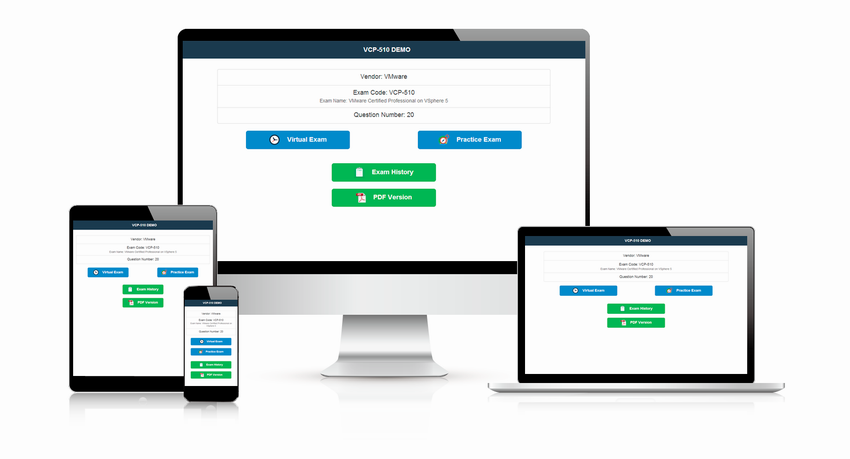
Long before you sit the ISO-IEC-27001-Lead-Auditor日本語 exam, you can judge the quality yourself: TorrentVCE publishes a free demo of the PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor日本語版) material, so you can test 418 practice questions, the online engine, and the study strategy before committing.
PECB ISO-IEC-27001-Lead-Auditor日本語 Exam Overview:
| Certification Vendor: | PECB |
|---|---|
| Exam Name: | PECB Certified ISO/IEC 27001 Lead Auditor Exam |
| Exam Number: | ISO-IEC-27001-Lead-Auditor |
| Available Languages: | French, English, Portuguese, German, Italian, Spanish |
| Exam Format: | Multiple choice questions, Scenario-based questions |
| Passing Score: | 70% |
| Real Exam Qty: | 60 |
| Certificate Validity Period: | 3 years |
| Exam Price: | $450 USD |
| Exam Duration: | 120 minutes |
| Related Certifications: | PECB Certified ISO/IEC 27001 Foundation PECB Certified ISO/IEC 27001 Lead Implementer |
| Recommended Training: | PECB ISO/IEC 27001 Lead Auditor Training Course |
| Exam Registration: | PECB Official Exam Registration |
| Sample Questions: |  |
| Exam Way: | Online proctored or onsite at authorized exam centers |
| Pre Condition: | Completion of PECB-certified ISO/IEC 27001 Lead Auditor training course; recommended prior knowledge of information security management systems and audit principles |
| Official Syllabus URL: | https://pecb.com/en/exam/iso-iec-27001-lead-auditor |
PECB ISO-IEC-27001-Lead-Auditor日本語 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Requirements of ISO/IEC 27001:2022 | 30% | - General requirements and ISMS scope definition
|
| Auditing Principles and Practices | 30% | - Audit preparation and planning
|
| Fundamental Concepts of Information Security | 15% | - Overview of ISO/IEC 27000 family of standards
|
| Information Security Controls (ISO/IEC 27002:2022) | 25% | - Control categories and implementation guidance
|
What Candidates Usually Ask Before Buying PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor日本語版)
PECB ISO/IEC 27001 Lead Auditor Training Course: Visit official page
Completion of PECB-certified ISO/IEC 27001 Lead Auditor training course; recommended prior knowledge of information security management systems and audit principles
The ISO-IEC-27001-Lead-Auditor日本語 exam contains 60 questions and lasts 120 minutes minutes, so pacing matters as much as knowledge. Practicing under a real timer on TorrentVCE helps you learn how long to spend on each item.
The PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor日本語版) material is written by a group of IT experts and certified trainers. Beyond assembling verified questions, they organize the bank into a study strategy for candidates, so you always know which section to tackle next instead of paging through questions at random.
The online engine recreates the atmosphere of the formal test, so the real ISO-IEC-27001-Lead-Auditor日本語 exam feels familiar rather than intimidating. It runs on Windows, Mac, Android, and iOS, places no limit on the number of installations, and lets you review at any time and from any location, which fits naturally around an IT worker's schedule.
The passing score of ISO-IEC-27001-Lead-Auditor日本語 is 70%, and the official exam fee is $450 USD. Knowing both numbers early helps you set a concrete target before you book the test.
This package includes 418 practice questions for the ISO-IEC-27001-Lead-Auditor日本語 exam. Every answer has been verified by our IT experts and certified trainers before release.
- Auditing Principles and Practices (30%)
- Fundamental Concepts of Information Security (15%)
- Requirements of ISO/IEC 27001:2022 (30%)
Study the sections in the order that matches your weakest areas first.
PECB Official Exam Registration: register for ISO-IEC-27001-Lead-Auditor日本語
PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor日本語版) Sample Questions:
シナリオ9
小規模なネットワーク企業であるCloudFortは、ネットワークセキュリティ、クラウドコンピューティング、仮想化ソリューションを提供しています。同社は最近、ISO/IEC 27001規格に基づく情報セキュリティマネジメントシステム(ISMS)の認証を取得し、その結果、認知度が急上昇し、CloudFortの事業運営の成熟度が証明されました。
CloudFortは、内部監査を実施することで、セキュリティ管理体制とISMS全体の有効性および効率性を継続的に見直し、強化してきました。しかし、その規模の大きさと、より高い客観性を求める姿勢から、経営陣は内部監査機能を外部委託することを決定しました。これにより、内部監査が監査対象業務から独立し、ISMSの継続的な改善において助言的な役割を果たすことが保証されます。
最初の認証監査後、同社はデータストレージソリューションを専門とする新部門を設立しました。この部門では、データセンター向けに最適化されたルーターやスイッチ、ネットワーク仮想化やネットワークセキュリティ機器などのソフトウェアベースのネットワーク機器を提供しました。新部門の設立に伴い、CloudFortはリスク評価プロセスと内部監査を開始しました。内部監査の結果、同社は新しいプロセスと管理体制の有効性と効率性を確認しました。
新設部署がISO/IEC 27001の要求事項を完全に満たしていることを確認した後、経営陣は同部署を認証範囲に含めることを決定しました。そして、同部署のプロセスとセキュリティ対策がISMS全体と完全に整合するように、認証範囲の拡大を認証機関に申請しました。
最初の認証監査から1年後、認証機関はCloudFortのISMSに対する再監査を実施しました。この監査の目的は、CloudFortのISMSがISO/IEC 27001の規定要件を満たしているかどうかを判断し、ISMSが継続的に改善されていることを確認することでした。監査チームは、認証されたISMSが規格要件を満たしていることを確認しました。しかしながら、新設された部署は、マネジメントシステム全体の運営方法に大きな影響を与える変更を導入したため、既存のプロセスと管理体制の更新が必要となりました。
さらに、CloudFortは認証範囲の拡大を申請したものの、新設部署がISMSに与える影響について、認証機関にタイムリーな情報提供を行わなかった。そのため、CloudFortの認証は停止された。
質問
CloudFort社は、新しい部門を含めるように認証範囲の拡大を要求しました。この状況をどのように分類しますか?シナリオ9を参照してください。
- A. 許容範囲内。多くの被監査者は、最初の認証では範囲を縮小し、その後、翌年以降に延長を申請することができます。
- B. 受け入れられません。なぜなら、拡張は最初の認証範囲に含まれているべきであり、大規模な再認証プロセスが実施されない限り、後から追加することはできないからです。
- C. 範囲を拡大するには組織全体の監査を再度行う必要があるため、受け入れられません。
Correct Answer: A 🗳️
Explanation: Only visible for TorrentVCE members. You can sign-up / login (it's free).
質問
組織がすべての受信トラフィックを管理するために単一のサーバーに依存している場合、潜在的な単一障害点が生じる可能性があります。サーバーに不具合やダウンタイムが発生すると、サービスが中断される可能性があります。
このシナリオはどのような状況を示しており、情報セキュリティのどの側面が主に影響を受けるのでしょうか?
- A. 可用性に影響を与えるリスク
- B. システムエラーが発生し、認証に影響が出ています
- C. 設定ミスにより、可用性に影響が出ています。
Correct Answer: A 🗳️
Explanation: Only visible for TorrentVCE members. You can sign-up / login (it's free).
監査結果とは、収集した監査証拠を監査基準に照らして評価した結果です。以下の監査証拠の形式案を評価し、許容できるものを2つ選択してください。
- A. ITマネージャーとシステムエンジニアの対話の音声録音
- B. 検証不可能なシステムエンジニアの発言
- C. 試験結果に対する署名のない手書きの変更
- D. 危険な活動の実施を実演する、以前に録画されたビデオの観察
- E. IT監査の結果に関する文書化された情報
- F. ITマネージャーによる事実陳述
Correct Answer: D,E 🗳️
Explanation: Only visible for TorrentVCE members. You can sign-up / login (it's free).
情報セキュリティインシデントが発生した場合、システムユーザーの役割と責任は遵守されなければならないが、以下の場合は例外とする。
- A. 必要に応じて証拠を保全する
- B. 必要に応じて捜査担当者に協力する
- C. 疑わしいまたは既知のインシデントを発見した場合は、サービスデスクを通じて報告してください。
- D. 情報セキュリティインシデントの詳細を全従業員に周知する
Correct Answer: D 🗳️
Explanation: Only visible for TorrentVCE members. You can sign-up / login (it's free).
情報セキュリティマネジメントシステムの監査をどのように実施すべきかを最も適切に表している選択肢を選んでください。
- A. 監査基準を用いて客観的な証拠を評価し、監査結果を生成する必要があります。その後、監査報告書を作成し、最終会議で監査チームリーダーに提出する必要があります。
- B. 監査目的を用いて監査証拠を評価し、監査結論を導き出す。そして、監査結果を作成し、最終会議で監査依頼者に提示する。
- C. 監査目的を用いて客観的な証拠を評価し、監査結論を導き出す必要があります。その後、監査勧告を作成し、経営陣レビューで経営陣に提示する必要があります。
- D. 監査結果を生成するために、状況証拠を評価するために監査基準を使用する必要があります。
次に、監査報告書を作成し、監査チーム会議で監査チームに提示する必要があります。 - E. 監査結果を生成するためには、客観的な証拠を評価するために監査手法を用いるべきである。その後、監査結論を作成し、最終会議で被監査者に提示すべきである。
- F. 監査勧告を作成するために、監査方法を用いて監査証拠を評価する必要がある。
次に、監査勧告を作成し、最終会議で被監査企業に提示する必要がある。
Correct Answer: E 🗳️
Explanation: Only visible for TorrentVCE members. You can sign-up / login (it's free).
Viewing page 1 out of 84 pages.
Viewing questions 1-5 out of 418 questions.
Related Exam
- ISO-IEC-27035-Lead-Incident-Manager VCE Torrent
- ISO-IEC-27001-Lead-Implementer-German VCE Torrent
- ISO-IEC-27001-Lead-Implementer VCE Torrent
- ISO-IEC-27001-Lead-Auditor-KR VCE Torrent
- ISO-IEC-27001-Lead-Auditor VCE Torrent
- ISO-IEC-27001-Lead-Auditor-Deutsch VCE Torrent
- ISO-IEC-27001-Lead-Auditor-CN VCE Torrent
- ISO-IEC-27001-Lead-Auditor日本語 VCE Torrent
Related Certifications
Over 95474+ Satisfied Customers
What Clients Say About Us
Try Before You Buy
Download a free sample of any of our exam questions and answers
- 24/7 customer support, Secure shopping site
- Free One year updates to match real exam scenarios
- If you failed your exam after buying our products we will refund the full amount back to you.
Quality and Value
TorrentVCE Practice Exams are written to the highest standards of technical accuracy, using only certified subject matter experts and published authors for development - no all study materials.
Tested and Approved
We are committed to the process of vendor and third party approvals. We believe professionals and executives alike deserve the confidence of quality coverage these authorizations provide.
Easy to Pass
If you prepare for the exams using our TorrentVCE testing engine, It is easy to succeed for all certifications in the first attempt. You don't have to deal with all dumps or any free torrent / rapidshare all stuff.
Try Before Buy
TorrentVCE offers free demo of each product. You can check out the interface, question quality and usability of our practice exams before you decide to buy.

To help our candidate solve the difficulty in Real Exam, we prepared the Most Reliable Valid Study Torrent for the Exam Preparation. Our aim is help our candidates realize their ability by practicing our Updated Practice Torrent.