Questions from this ECSAv10 dump are 90% valid... not all answers. I passed this exam a few days ago and got these results.
 Neil


A EC-COUNCIL credential turns 'familiar with' into 'certified in.' In 2026, TorrentVCE's EC-COUNCIL EC-Council Certified Security Analyst (ECSA) v10 : Penetration Testing practice questions get you through the ECSAv10 exam with your schedule — and your sanity — intact.
| Certification Vendor: | EC-Council |
|---|---|
| Exam Name: | ECSA v10: Penetration Testing |
| Exam Number: | 712-50 (commonly associated; may vary by region/version) |
| Exam Price: | USD 400–950 (varies by region and bundle) |
| Real Exam Qty: | Approximately 150 (varies by delivery format) |
| Exam Duration: | 240 minutes |
| Exam Format: | Multiple Choice Questions, Practical/Lab-based assessment (iLabs environment), Scenario-based penetration testing tasks |
| Passing Score: | Approximately 70% (varies by exam version) |
| Available Languages: | English |
| Certificate Validity Period: | 3 years |
| Related Certifications: | Licensed Penetration Tester (LPT) Certified Ethical Hacker (CEH) |
| Recommended Training: | EC-Council Official ECSA Training & iLabs |
| Exam Registration: | EC-Council Official Certification Registration |
| Sample Questions: |  |
| Exam Way: | Online proctored exam or authorized EC-Council testing center (may include practical lab environment depending on delivery mode) |
| Pre Condition: | Recommended: EC-Council Certified Ethical Hacker (CEH) or equivalent knowledge of ethical hacking and networking fundamentals |
| Official Syllabus URL: | https://www.eccouncil.org |
| Section | Objectives |
|---|---|
| Topic 1: Reporting and Documentation | - Risk analysis and remediation recommendations - Penetration testing report writing |
| Topic 2: Web Application Penetration Testing | - Injection and session management flaws - OWASP Top 10 vulnerabilities |
| Topic 3: Vulnerability Analysis | - Vulnerability identification techniques - Exploitation feasibility analysis |
| Topic 4: Wireless Network Security Testing | - Wi-Fi attack vectors and exploitation - Wireless encryption weaknesses |
| Topic 5: Social Engineering and Human Factors | - Phishing and pretexting techniques - Human vulnerability exploitation |
| Topic 6: System Hacking and Exploitation | - Password attacks and system compromise methods - Privilege escalation techniques |
| Topic 7: Introduction to Penetration Testing Methodologies | - Information security assessment lifecycle - Penetration testing frameworks and standards |
| Topic 8: Network Scanning and Enumeration | - Active and passive reconnaissance - Port scanning and service identification |
The ECSAv10 exam is EC-COUNCIL's official assessment for the EC-Council Certified Security Analyst (ECSA) v10 certification, which sits at the Professional level. It verifies that you can work with the EC-COUNCIL EC-Council Certified Security Analyst (ECSA) v10 : Penetration Testing skill set the way real jobs demand — not merely recognize the terminology. It also belongs to a certification family that includes Certified Ethical Hacker (CEH), Licensed Penetration Tester (LPT), so passing it strengthens your position across multiple career paths. For newcomers and veterans alike, the ECSAv10 exam is the kind of credential that converts effort into evidence.
The EC-COUNCIL EC-Council Certified Security Analyst (ECSA) v10 : Penetration Testing blueprint contains 8 domains, beginning with Vulnerability Analysis, Web Application Penetration Testing, and Reporting and Documentation. Use the weightings like a map of where the points live — the heaviest domains earn the largest share of your study hours. The complete topic list is in the exam topics section above; study against it, and nothing in the exam will feel unannounced.
You're looking at Approximately 150 (varies by delivery format) questions inside 240 minutes on the EC-COUNCIL EC-Council Certified Security Analyst (ECSA) v10 : Penetration Testing exam. Do the division now and memorize your per-question budget; on exam day, anything that blows its budget gets flagged and revisited with leftover time. Timed practice is what makes this instinctive — the TorrentVCE PC test engine runs time-limited mock exams and scores them automatically, so you arrive already knowing your pace.
EC-COUNCIL sets the EC-COUNCIL EC-Council Certified Security Analyst (ECSA) v10 : Penetration Testing passing score at Approximately 70% (varies by exam version), and each attempt costs USD 400–950 (varies by region and bundle) — full price every time, retakes included. That makes preparation the cheaper strategy by a wide margin. The practical path: take auto-scored timed mocks with TorrentVCE practice questions until you clear the passing mark comfortably across multiple runs, then register with confidence grounded in data.
The official EC-COUNCIL EC-Council Certified Security Analyst (ECSA) v10 : Penetration Testing format list includes: Multiple Choice Questions, Practical/Lab-based assessment (iLabs environment), Scenario-based penetration testing tasks. Each format rewards a specific skill — scenario items reward careful reading order, multi-select items reward completeness — so practice should cover all of them, not just your favorites. TorrentVCE's 205 practice questions span the full list, which means the exam's mechanics feel rehearsed and only its content requires thought.
EC-COUNCIL offers the ECSAv10 exam in English. Choose the language you process fastest when the clock is running — comprehension speed quietly decides borderline results. If English is your pick, working through TorrentVCE's English ECSAv10 practice questions builds precisely the vocabulary the exam will use against you.
Passing the EC-COUNCIL EC-Council Certified Security Analyst (ECSA) v10 : Penetration Testing exam earns a credential valid for 3 years. Record the expiry date as soon as you pass, and look into recertification options well in advance — a renewal planned early is trivial, a lapsed credential is not. Recertification policy belongs to EC-COUNCIL and changes periodically, so confirm the current rules on the official certification page.
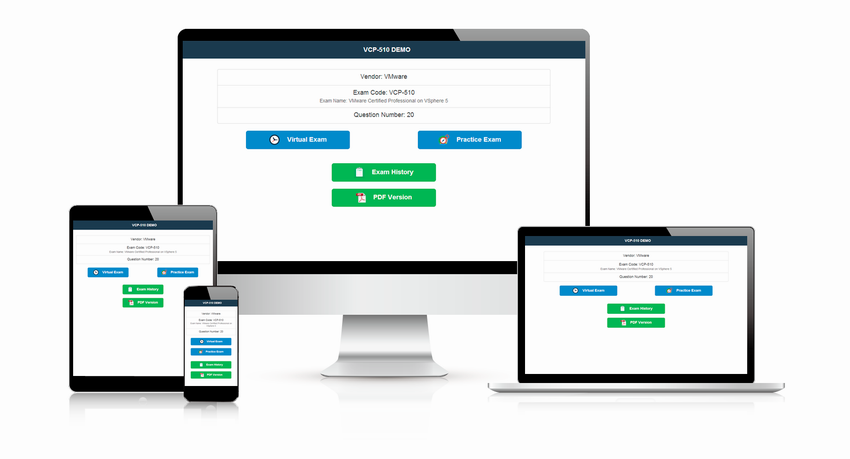
Three modes, one content set — 205 expert-written questions in each:
A phone alone can carry your entire review load — the lightest schoolbag you'll ever own.
Yes. TorrentVCE's free EC-COUNCIL EC-Council Certified Security Analyst (ECSA) v10 : Penetration Testing PDF demo contains genuine sample questions with full explanations, so you can verify the quality before paying. Every purchase includes 365 days of free updates; after that, renewing costs just 50% of the regular price from your member zone. Try it first — informed candidates are our favorite kind.
Our experts track EC-COUNCIL's blueprint changes continuously and revise the EC-COUNCIL EC-Council Certified Security Analyst (ECSA) v10 : Penetration Testing material to match — your purchase includes 365 days of free updates through your member zone. Watch the New Releases section or the TorrentVCE newsletter, and always confirm your version 3-4 days before your exam. If a product expires, repurchasing at 50% off restarts the update service immediately.
Completely. Some candidates worry — reasonably — about virus-laden downloads from unknown sites. TorrentVCE products are formal education materials: dedicated staff safeguard all information, McAfee security services protect every transaction, and your personal data is never shared with third parties. From purchase to download to daily use, your safety is covered at every step.
Delivery: your EC-COUNCIL EC-Council Certified Security Analyst (ECSA) v10 : Penetration Testing practice questions are downloadable instantly and emailed within one minute of payment — if 2 hours pass, check spam and contact support. Installs are unlimited. Refund: the 100% Money Back Guarantee covers you if you take the corresponding exam within 60 days of purchase and don't pass — submit a scanned enrollment slip and your official Score Report PDF within 2 days after the exam, and the full refund processes within 7 days. Excluded: attempts within 3 days of purchase, exams never actually taken, free items, and expired orders; candidate and payer names must match. Prefer a different trade? Exchange for two free exam products of equal value and keep your update service.
Judge the material first with the free demo. When you buy, your ECSAv10 product is downloadable instantly and emailed within one minute of payment — contact support if 2 hours pass — with unlimited installations across your computers. Every transaction is protected by McAfee security services, downloads are safe, your information is never shared, and 365 days of free updates keep the content aligned with the live exam.
Spend half the time and keep all of the coverage: download the free ECSAv10 demo, and let TorrentVCE's 205 practice questions make your EC-COUNCIL EC-Council Certified Security Analyst (ECSA) v10 : Penetration Testing preparation the efficient part of your week.
You setup SNMP in multiple offices of your company. Your SNMP software manager is not receiving data from other offices like it is for your main office. You suspect that firewall changes are to blame.
What ports should you open for SNMP to work through Firewalls.
(Select 2)
Correct Answer: A,D 🗳️
Which of the following external pen testing tests reveals information on price, usernames and passwords, sessions, URL characters, special instructors, encryption used, and web page behaviors?
Correct Answer: A 🗳️
Which one of the following acts related to the information security in the US fix the responsibility of management for establishing and maintaining an adequate internal control structure and procedures for financial reporting?
Correct Answer: B 🗳️
ARP spoofing is a technique whereby an attacker sends fake ("spoofed") Address Resolution Protocol (ARP) messages onto a Local Area Network. Generally, the aim is to associate the attacker's MAC address with the IP address of another host (such as the default gateway), causing any traffic meant for that IP address to be sent to the attacker instead.
ARP spoofing attack is used as an opening for other attacks.
What type of attack would you launch after successfully deploying ARP spoofing?
Correct Answer: A 🗳️
SQL injection attacks are becoming significantly more popular amongst hackers and there has been an estimated 69 percent increase of this attack type.
This exploit is used to great effect by the hacking community since it is the primary way to steal sensitive data from web applications. It takes advantage of non-validated input vulnerabilities to pass SQL commands through a web application for execution by a back-end database.
The below diagram shows how attackers launched SQL injection attacks on web applications.
Which of the following can the attacker use to launch an SQL injection attack?
Correct Answer: C 🗳️
Over 95472+ Satisfied Customers
Questions from this ECSAv10 dump are 90% valid... not all answers. I passed this exam a few days ago and got these results.
Neil
ECSAv10 exam was so easy.
 Rachel

Passed my ECSAv10 certificataion exam recently using the exam guide pdf files by TorrentVCE. Valid study material. Thank you TorrentVCE.
 Troy
Valid ECSAv10 exam braindumps! Only about 3 new questions come out. I have taken ECSAv10 exam and got the certificate. Next time I still choose to use your dumps. Thanks so much!
 Rita
I just passed ECSAv10 exam. I trusted TorrentVCE exam dumps and I will recommend your website to all who want to pass their exams. Thanks so much for your help!
 Amos

Thanks for your great EC-COUNCIL support and cool dumps.
 Frank
I took the ECSAv10 test today,and passwed with these ECSAv10 exam question, so this is valid.
 Wallis
Thank you for providing me the great EC-COUNCIL dumps.
 Ella
The ECSAv10 exam braindumps contain a good set of questions. I studied the dump over and over, as they predicted that I passed the ECSAv10 exam. Thanks to all of you!
 Zara
I got my ECSA certification.
 Denise
Previously I was very nervous about my ECSAv10 test wiped off this stress by providing me with a complete guidance regarding ECSAv10.
 Elva
As soon as I found TorrentVCE was relaxed to know that from onwards I am going to get handy and reliable helping material for ECSAv10 exam.
 Brook
I doubt the answers to the questions, but as they told me the pass rate is 100%, so i chose to trust them, and i really passed the ECSAv10 exam. Thank you for your kind support!
 Nina
Since the exam cost is high, I want to pass ECSAv10 at first trial, I buy this dumps. And this id a right choise. Pass exam easily.
 Merle
I get raise after passing ECSAv10. what a coincidence! This certification is very important for my company.
 Sebastiane
One of my friend shared me the ECSAv10 study guide, after using it, i passed it.
 Carey
The dumps from TorrentVCE is very helpful for me. I recently purchased ECSAv10 exam pdf dumps from TorrentVCE and passed the exam sucessfully with good score. Thanks very much!
 Tracy
TorrentVCE Practice Exams are written to the highest standards of technical accuracy, using only certified subject matter experts and published authors for development - no all study materials.
We are committed to the process of vendor and third party approvals. We believe professionals and executives alike deserve the confidence of quality coverage these authorizations provide.
If you prepare for the exams using our TorrentVCE testing engine, It is easy to succeed for all certifications in the first attempt. You don't have to deal with all dumps or any free torrent / rapidshare all stuff.
TorrentVCE offers free demo of each product. You can check out the interface, question quality and usability of our practice exams before you decide to buy.
To help our candidate solve the difficulty in Real Exam, we prepared the Most Reliable Valid Study Torrent for the Exam Preparation. Our aim is help our candidates realize their ability by practicing our Updated Practice Torrent.
